Archives for ITConsulting

Building a New Business Network the Right Way – From the Ground Up

I’ve been working on the IT infrastructure design for a new business, with a focus on performance, security, reliability and future expansion.

For me, a good IT setup isn’t just about buying equipment and plugging everything in. It’s about understanding how the business will operate, choosing the right technology and designing an infrastructure that will support it for years to come.

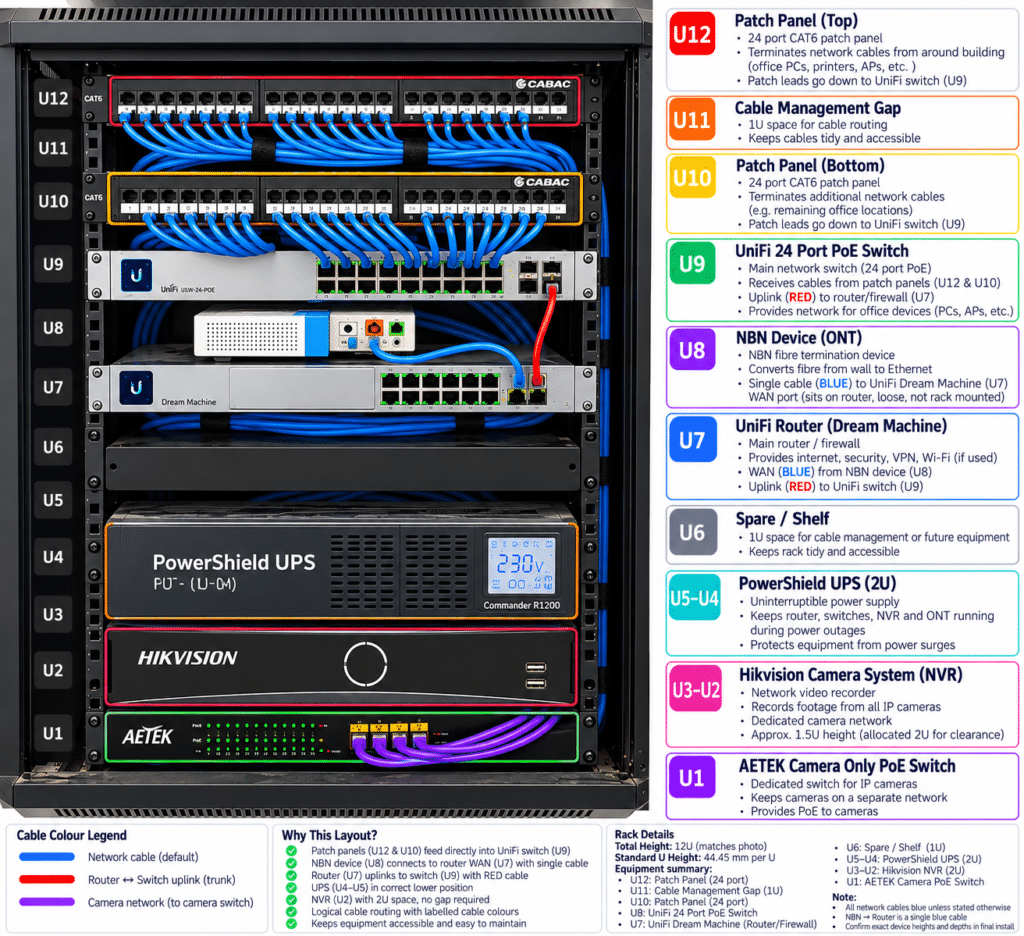
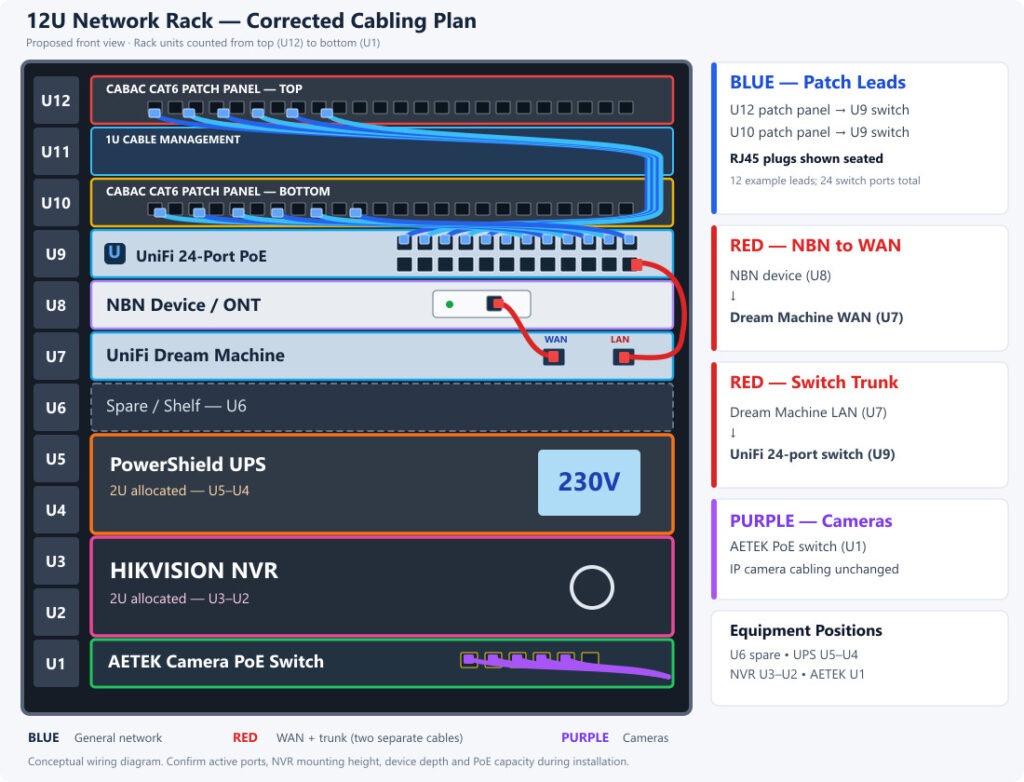
πŸ’‘ BOSS IT 12U RACK Network Design

cramminga12urack

We have chosen to build this network around the Ubiquiti UniFi ecosystem, providing centralised management, enterprise-grade networking features and the flexibility to expand as the practice grows.

Network Infrastructure Design – Layer 2/3, VLANs, Security & 10Gb DAC

The design is based around a UniFi Dream Machine SE firewall/router and a UniFi Pro 24-port PoE managed switch, connected through a 10Gbps SFP+ DAC uplink. This provides a high-capacity backbone between the switching and routing infrastructure, with centralized management and room for future growth.

One of the main considerations is Layer 2 and Layer 3 network segmentation using VLANs. Rather than having everything on one flat network, I’m planning separate VLANs for corporate devices, network management, guest Wi-Fi, CCTV and other equipment. At Layer 2, VLANs separate broadcast domains, while Layer 3 routing through the firewall allows communication between networks to be controlled using specific security policies.

For example, guest Wi-Fi should have internet access but no access to internal workstations or management interfaces. Likewise, CCTV equipment shouldn’t have unrestricted access to the corporate network. This is where inter-VLAN firewall rules, access control and the principle of least privilege become important. A separate VLAN or physical switch alone doesn’t guarantee security; the routing and firewall configuration are what enforce the restrictions.

The setup also incorporates Wi-Fi 7 access points, PoE distribution, structured CAT6 cabling, dedicated CCTV switching and UPS protection. I’ve also considered the limitations of the hardware, including 1Gbps access ports, PoE budgets, firewall throughput and how the 10Gbps backbone fits into the overall design.

Even the physical rack layout has been planned around cable management, equipment placement, accessibility and future maintenance. Once installed, the important part will be validating VLAN isolation, firewall policies, routing, DHCP, wireless coverage, uplink performance and recovery procedures.

There’s a big difference between installing networking equipment and actually designing a network properly.
Untitled

Beyond OneDrive: Engineering a Secure Microsoft 365 Cloud Integration

Sometimes a seemingly simple IT requirement demands enterprise-level cloud architecture rather than an off-the-shelf solution.

A recent project at BOSS IT SOLUTIONS involved integrating an existing industrial business system with Microsoft 365 SharePoint, allowing operational reports to be transferred securely and automatically to the cloud.

The challenge wasn’t simply uploading files. It was designing a solution that respected the security, operational and multi-user requirements of the existing environment.

The challenge: An industrial PC, not an office workstation

The computer was configured as a dedicated industrial workstation, using local Windows accounts to operate specialised business applications.

However, authorised staff also needed occasional access for meetings and other business activities.

Using Windows’ Switch User functionality, staff could access separate profiles while the industrial applications continued running in their original session.

The reporting integration also needed to operate independently in the background, regardless of which user was signed in.

Connecting the machine to an employee’s OneDrive wasn’t appropriate. That would introduce unnecessary access to company information, dependencies on individual Microsoft 365 accounts and potential authentication or synchronisation problems.

The requirement was to connect the machine to the cloud without compromising its primary industrial purpose.

The solution: Application-to-cloud architecture

I designed and developed a dedicated integration using technologies and security principles commonly found in enterprise cloud environments, including AWS and Microsoft Azure.

The architecture incorporated:

  • Microsoft Entra ID: A dedicated application identity, independent of employee accounts.
  • Certificate-based authentication: Secure, passwordless application authentication using an installed private key.
  • Microsoft Graph REST API: Direct communication with SharePoint Online, without OneDrive synchronisation.
  • Least-privilege access: Application permissions restricted to a specific SharePoint reporting folder.
  • PowerShell 7: Custom file-processing, API communication, duplicate detection, overwrite protection and error logging.
  • Windows Task Scheduler: Unattended execution under a controlled local Windows account.
  • Windows security management: Certificate private-key permissions, local security policies and multi-user session management.

The integration operates independently of interactive Microsoft 365 sessions and leaves the existing industrial software and original reporting files untouched.

More than a PowerShell script

The complexity was in getting several different technologies and security boundaries working together reliably.

This required configuring cloud application identities, establishing certificate trust, assigning granular resource permissions, working directly with REST API endpoints and troubleshooting Windows authentication and scheduled execution.

Conceptually, this is similar to AWS cloud integration architecture: a dedicated application identity, resource-specific authorisation, API-based communication and automated workloads operating independently of human users.

Rather than simply synchronising files, the solution establishes a controlled, authenticated connection between an on-premises business system and a cloud service.

The outcome

Historical reports were successfully transferred to SharePoint, and unattended uploads were tested and verified through Windows Task Scheduler.

The solution provides centralised reporting, duplicate protection, operational logging and secure cloud access without requiring employee Microsoft 365 credentials on the industrial workstation.

Meanwhile, the computer retains its operational role and supports authorised staff using separate Windows profiles.

Why this matters

Many businesses operate specialised systems that don’t natively integrate with modern cloud platforms.

Replacing those systems isn’t always practical or necessary.

With the right combination of cloud architecture, identity management, Windows engineering, API development and automation, existing systems can be extended securely without disrupting the business.

At BOSS IT SOLUTIONS, this is the level of technical problem-solving I bring to business IT: designing solutions that go well beyond everyday computer support.